

Applications
An application is any service protected by Ironchip: a web portal through OIDC or SAML, a VPN through RADIUS, or your own application through the HTTP API. This page explains how to add one in the admin console, how to create an HTTP-MFA integration, and how to grant access to users and groups.
Add an application to the company
Section titled “Add an application to the company”The Applications section lists all the protected services added to Ironchip, with their integration type (Integration column).
-
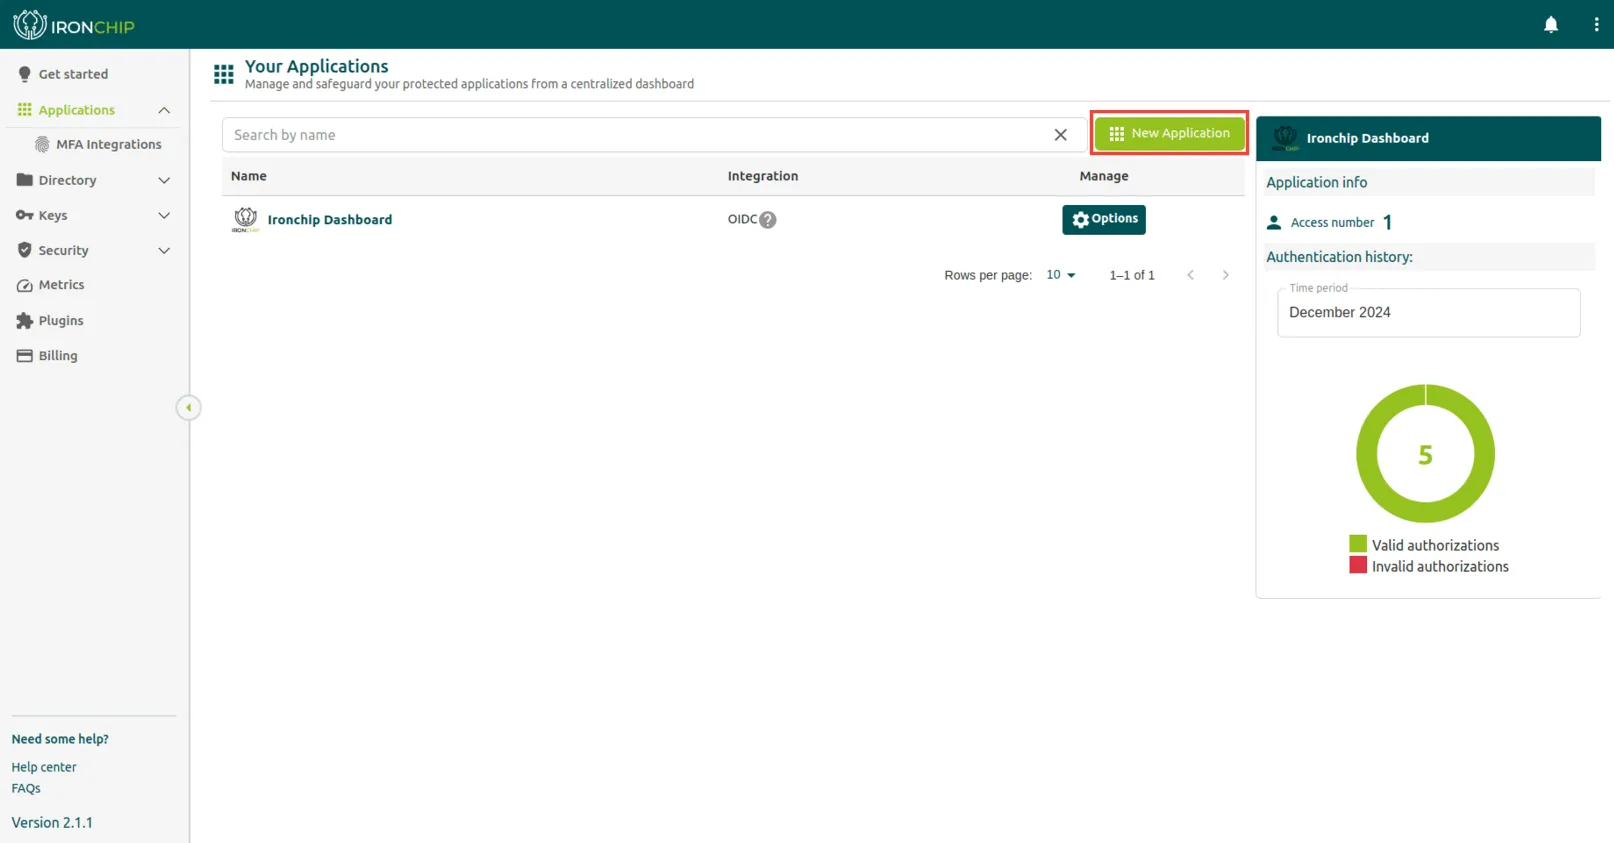
Go to Applications and click New application. The Add new application window opens.
-
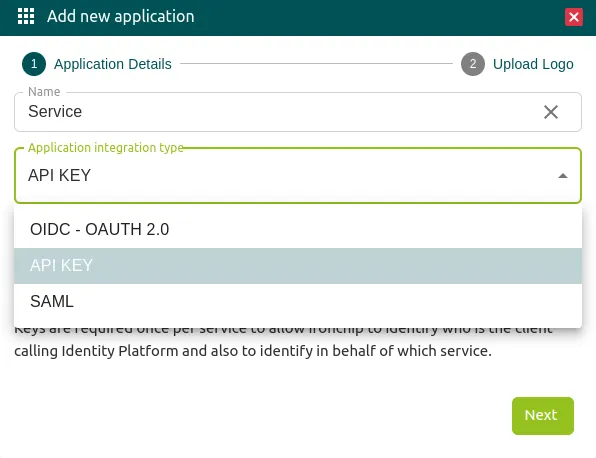
In the Application Details step, enter the application name in Name and choose the type in Application integration type, for example OIDC - OAUTH 2.0, API KEY, or SAML. Click Next.
-
Complete the Upload Logo step to finish. The application appears in the Applications list.
Create an HTTP-MFA integration
Section titled “Create an HTTP-MFA integration”HTTP-MFA is an integration type that the administrator creates first, so that services of that type can be created afterwards.
-
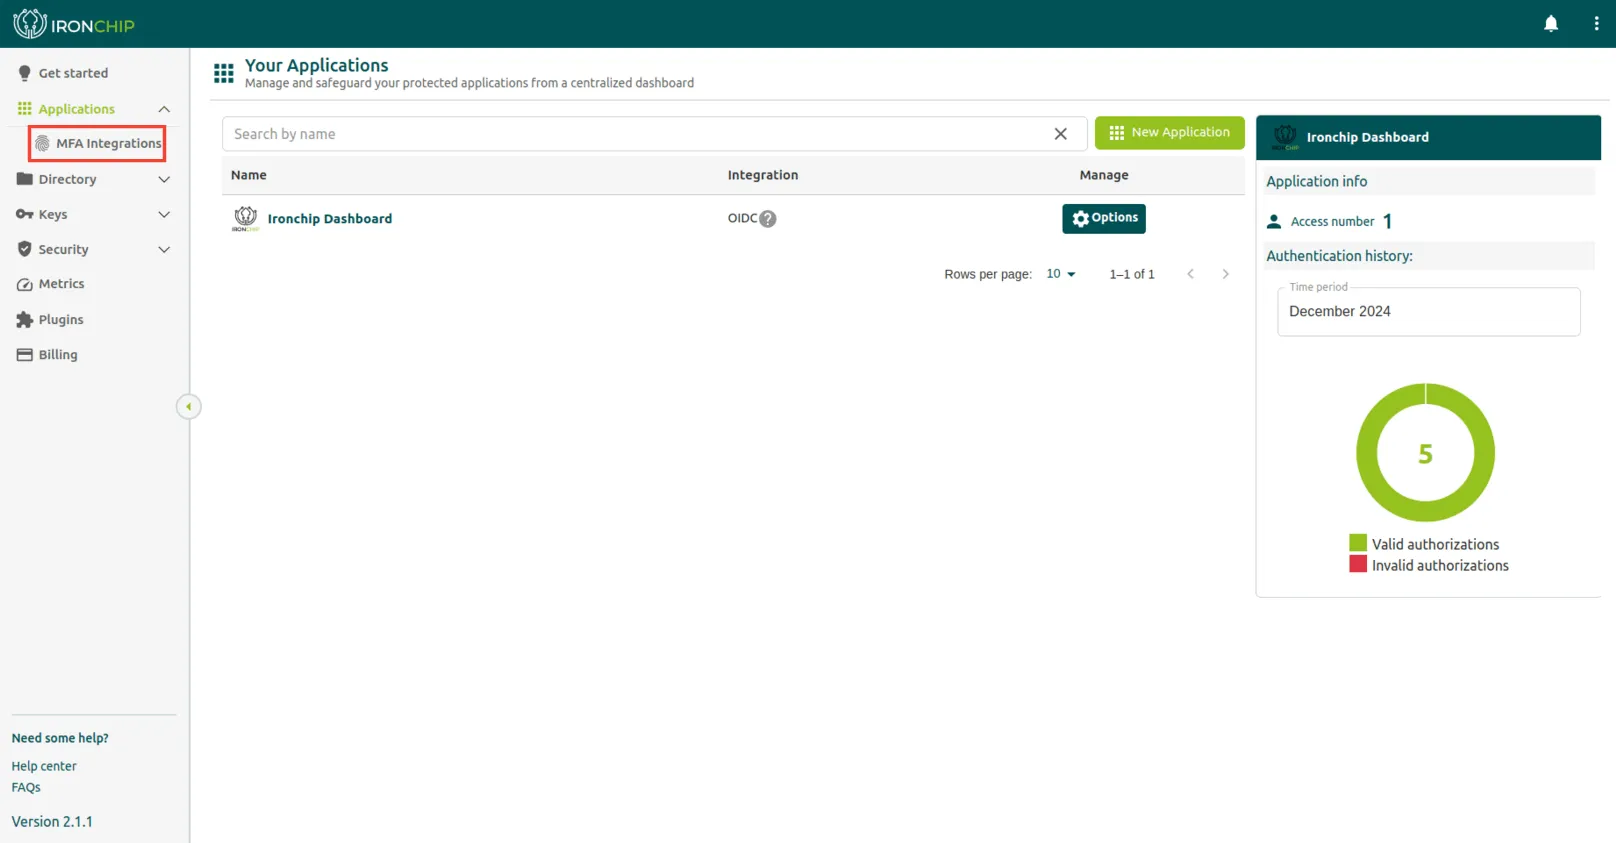
Expand Applications in the left menu and click MFA integrations.
-
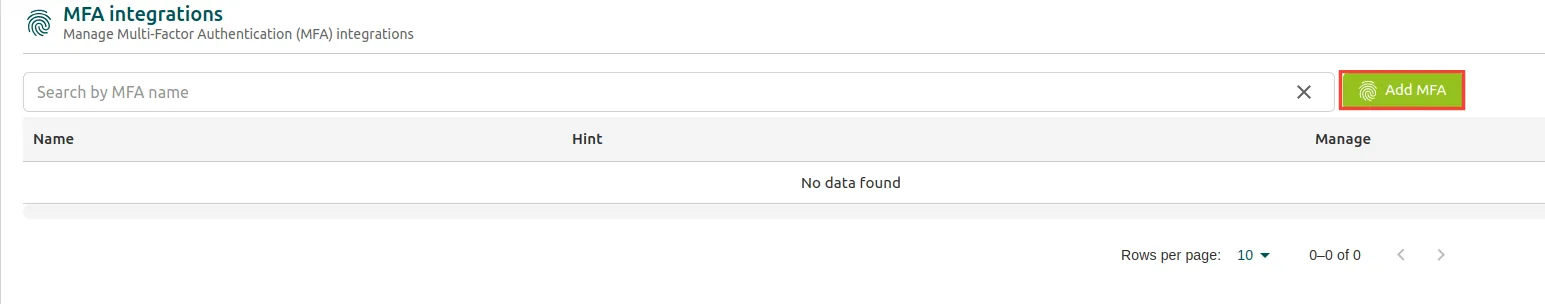
Click Add MFA.
-
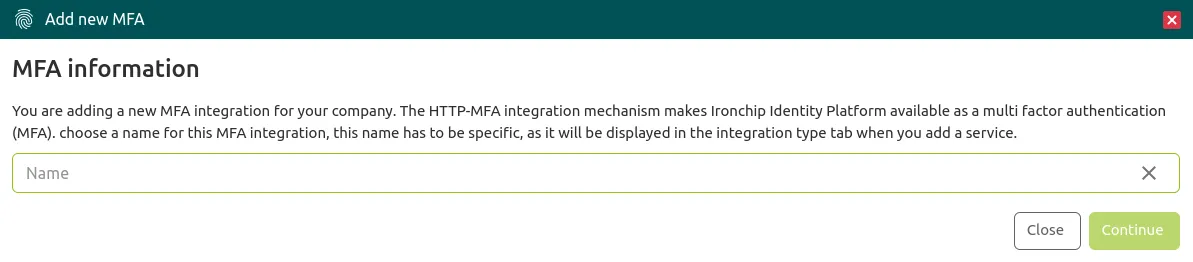
In the Add new MFA window, fill in the Name field and click Continue. Choose a name that is easy to recognize: it is the one that appears in Application integration type when you add an application.
These two videos show how to create an MFA application and how to reference it from a service. They were recorded with an earlier version of the console, so some menu names have changed.
Grant access to users and groups
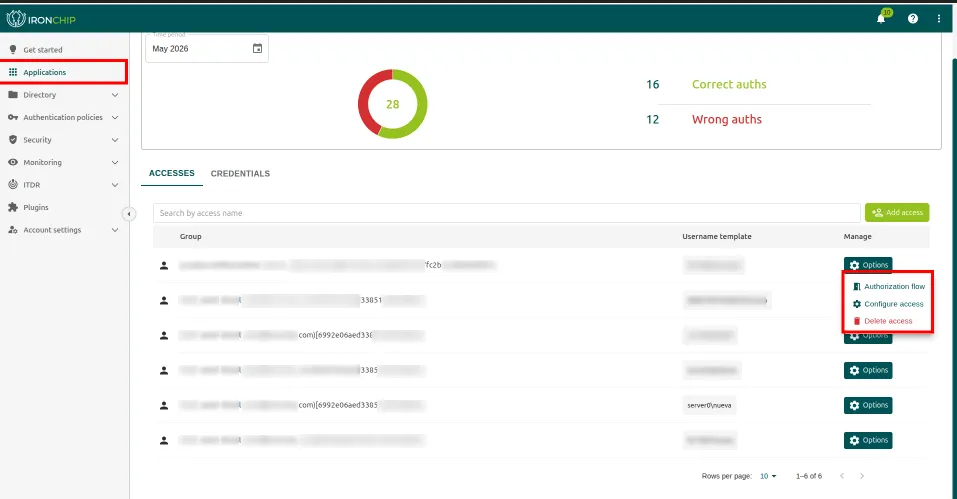
Section titled “Grant access to users and groups”To grant access to an application, go to Applications and select the application you want to add one or more users or groups to. The application information page shows the count of successful and failed authentications and the list of groups and users that already have access configured.
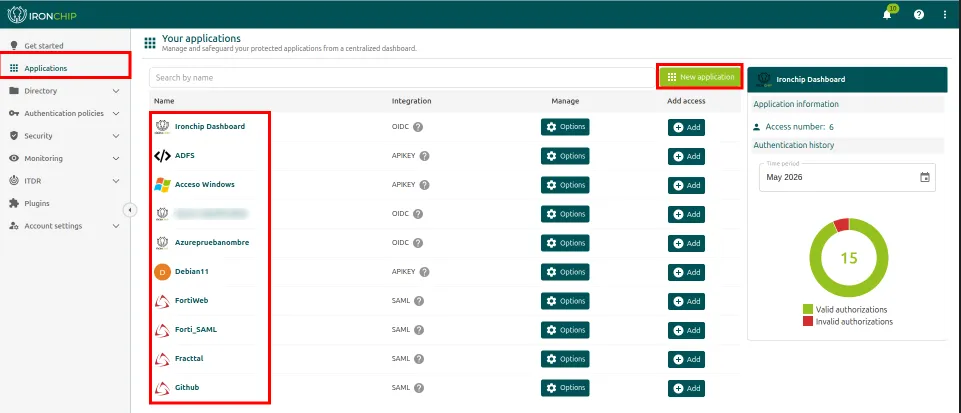
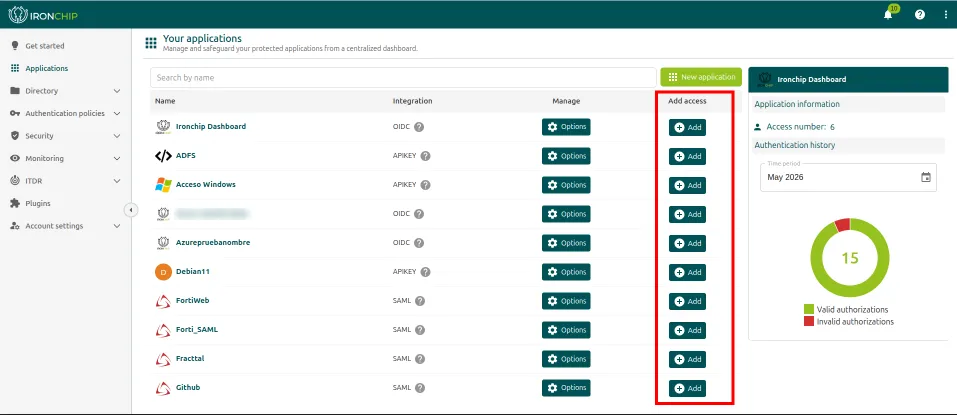
To grant new access, click Add, to the right of the application, in the Add access column.
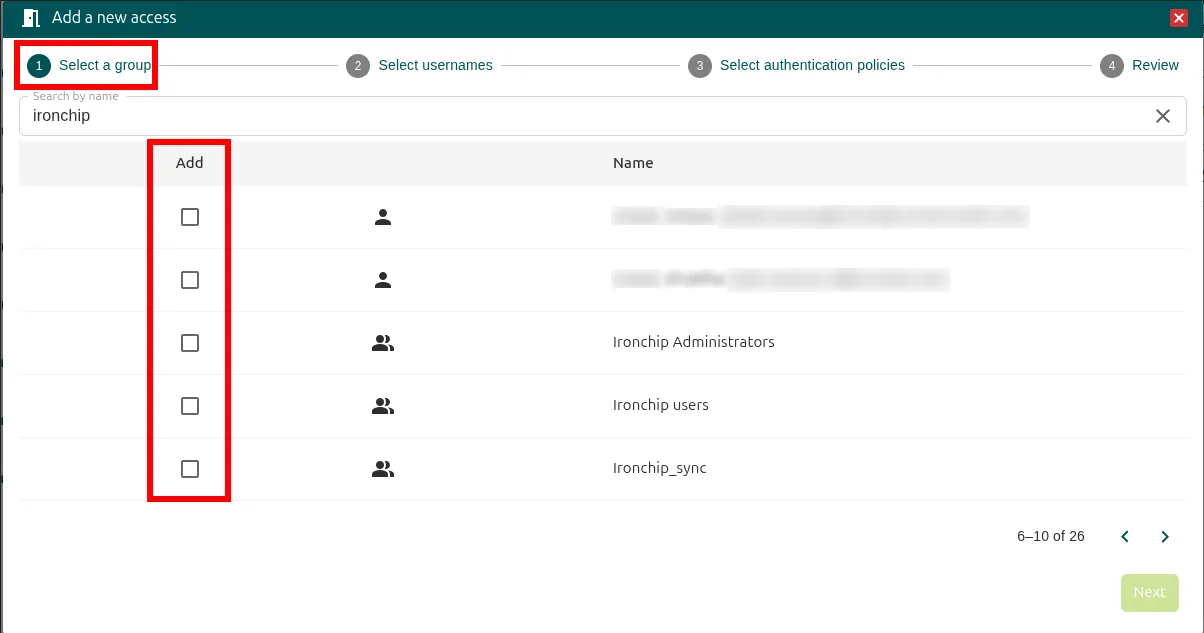
The Add a new access window opens, with four steps.
Step 1: Select the user or group
Section titled “Step 1: Select the user or group”In Select a group, check the box to the left of each group or user you want to grant access to and click Next. The list shows the groups and users of the company.
Step 2: Define the username format
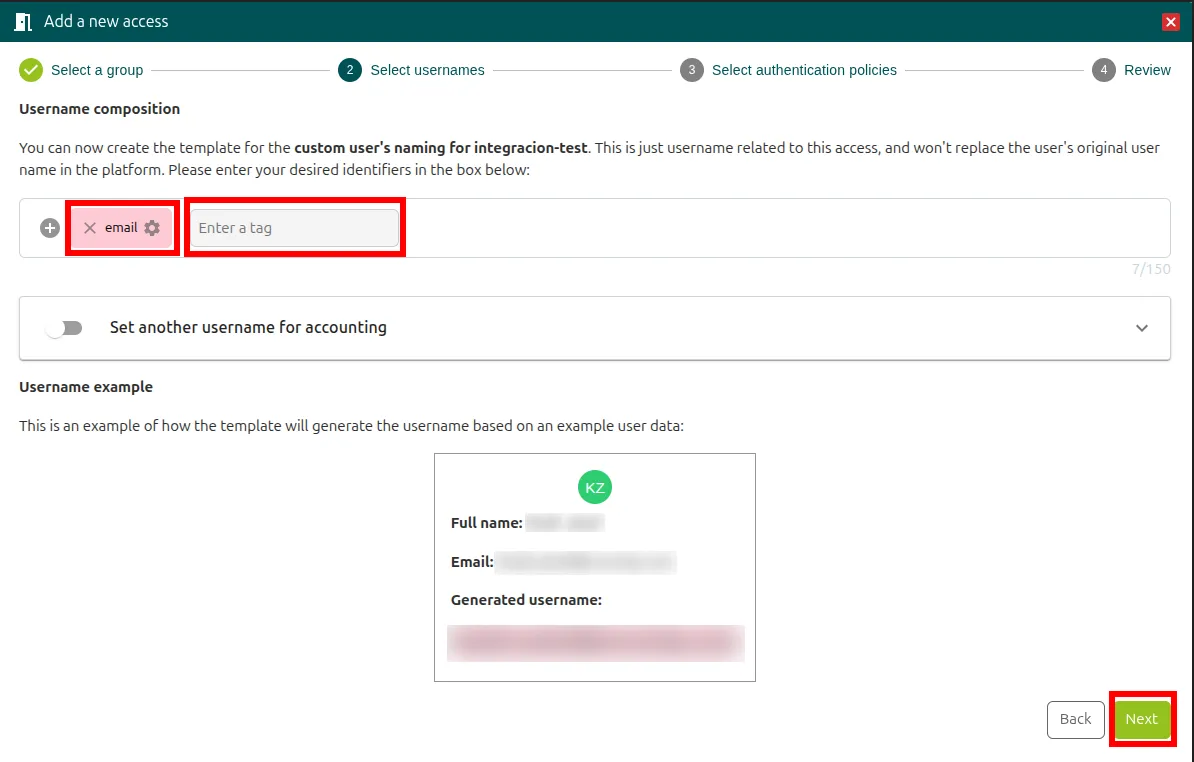
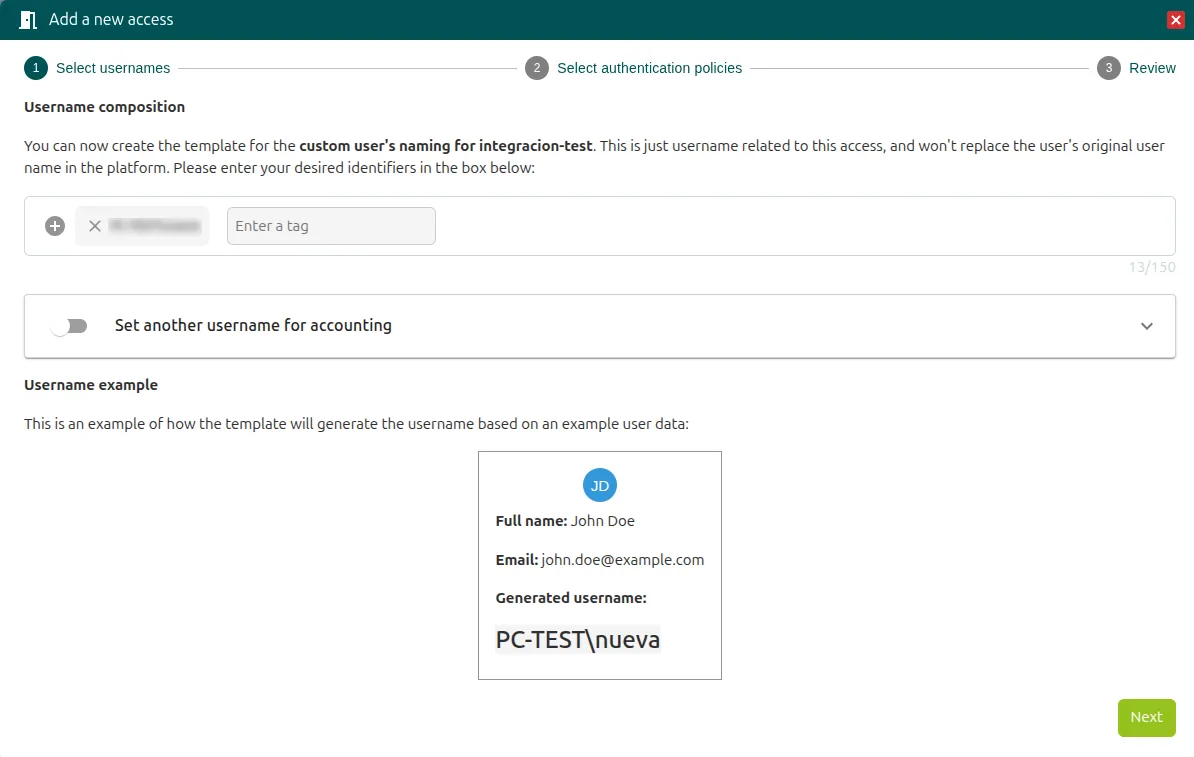
Section titled “Step 2: Define the username format”In Select usernames you choose the format of the external username (External Username) used to access the application. This username applies only to this access: it does not replace the user’s name on the platform.
By default, email is selected, but you can combine tags (name, surname, domain…) to customize it. Click Enter a tag to see the available tags. With tags, each user gets a different username; if you use a static template, the same username applies to all users. Below, Username example shows the username the template would generate from the data of a sample user.
If you turn on Set another username for accounting, you can define a different username for the accounting of this access. Click Next when you finish.
Step 3: Choose the authentication methods
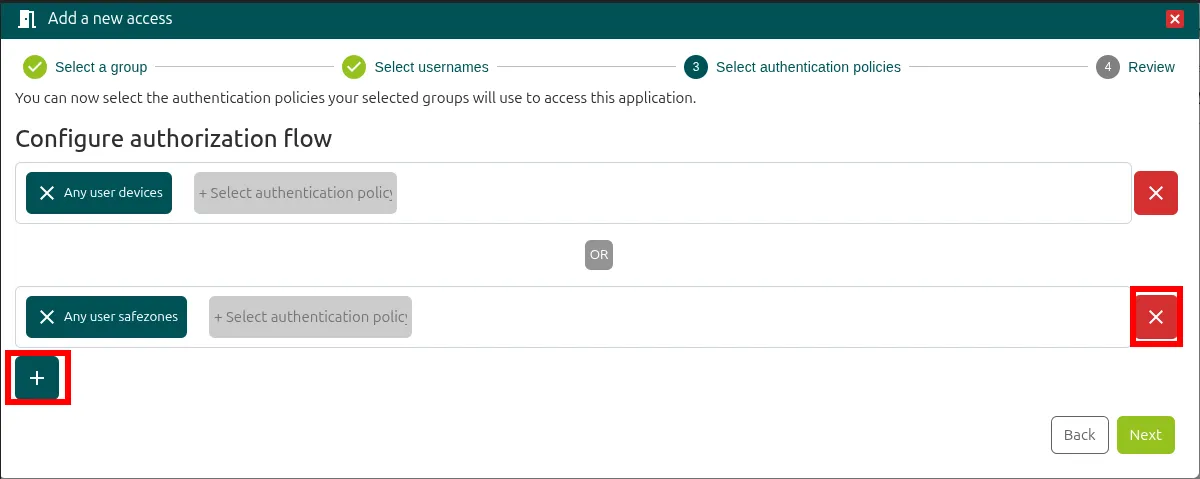
Section titled “Step 3: Choose the authentication methods”In Select authentication policies, select the authentication method assigned to the group or user. These are the company’s authentication policies. You can combine several on the same line:
- AND: all the selected conditions must be met.
- OR: at least one of them must be met.
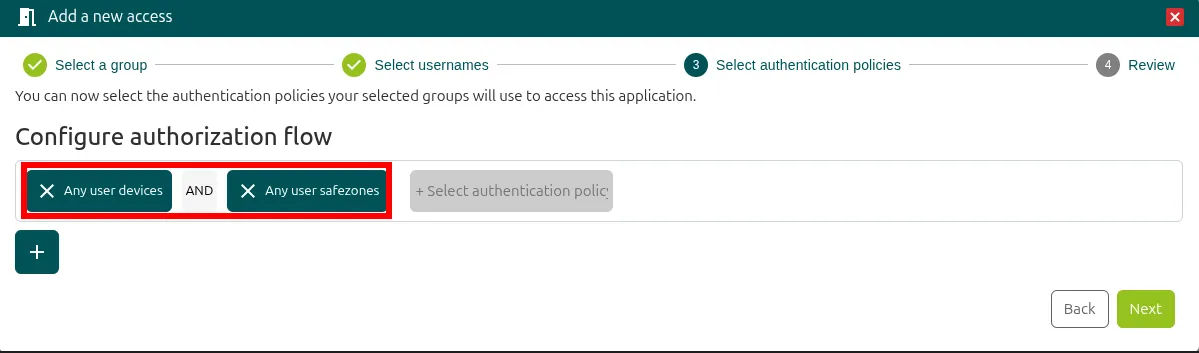
Use the + button to add methods and the x button to remove the ones you do not want. Click Next when you finish.
Step 4: Review the summary
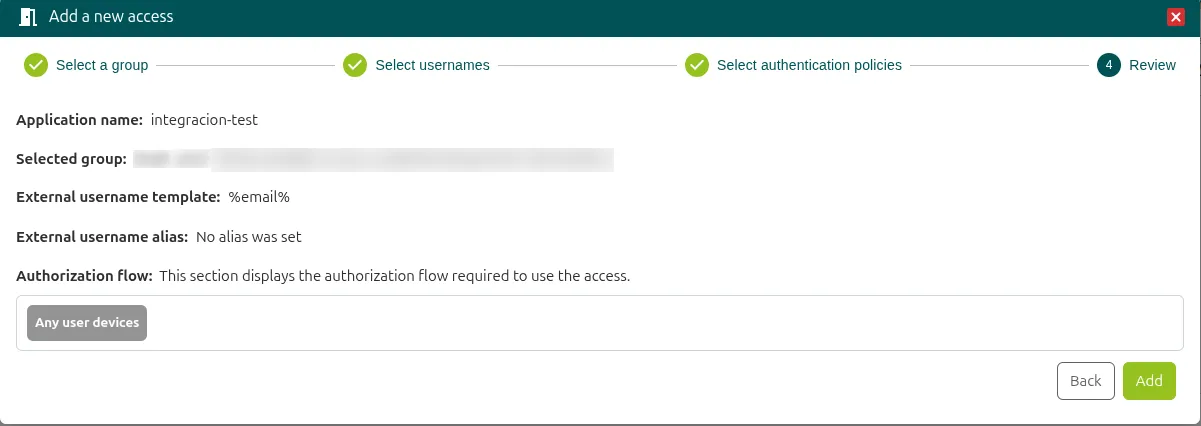
Section titled “Step 4: Review the summary”Review shows the application name, the selected group or user, the external username template, and the authorization flow (Authorization flow) the access requires. Check the data and click Add to create the access.
Manage an access
Section titled “Manage an access”When the process ends, the access appears in the Accesses tab of the application. You can manage it at any time with the Options button:
-
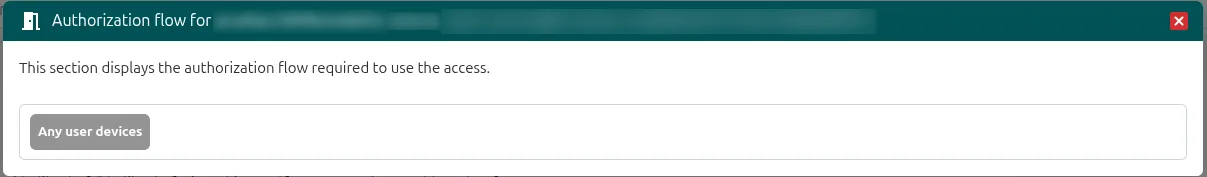
Authorization flow: shows a summary of the access conditions, that is, the configured rules. Close the window to exit.
-
Configure access: lets you modify the access starting from step 2.
-
Delete access: permanently deletes the access.
Was this page helpful?
Thank you. We will use it to improve the documentation. If you want to tell us what is missing or unclear, write to support@ironchip.com.