

Evidence and decisions
The fraud engine backs each risk level with evidence (which sensors matched the user’s known context) and decisions (which fraud or legitimate usage pattern was detected). For the risk levels and the evidence blocks shown in the console, see Risk assessment.
Sensor match type
Section titled “Sensor match type”| Match type | Description |
|---|---|
gps |
Comparison using GPS data. |
wifi_scan |
Comparison using visible Wi-Fi networks, with no matching connected network. |
wifi_connection |
Comparison using the Wi-Fi network the device is connected to. |
mobile_networks |
Comparison using the connected mobile networks. |
Decisions
Section titled “Decisions”Ironchip’s APIs also base risk assessments on decisions, which come from different analyses through different lenses. Decisions arrive in the event.fraud_cases field of the report. The following table describes the possible decision values and their meaning.
| Decision | Description |
|---|---|
| SIM Swapping / ATO | Account takeover detected, with or without a SIM swap, depending on the protection of the customer’s user. |
| Phishing | Phishing attack detected from a specific location (multiple ATOs). |
| Synthetic identity | Synthetic identity attack detected. |
| New user | New user detected on the Ironchip platform. |
| Location fraud | Location fraud attempt detected by comparing all location data sources. |
| Banned location | Location detected in a banned place, for example, a location detected in Russia. |
| Device swapping | Legitimate device swap detected for a user. |
| Location swapping | Legitimate location swap detected for a user. |
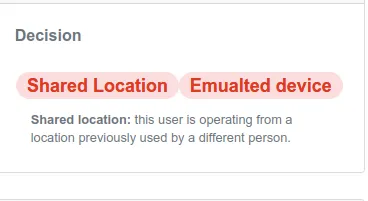
| Shared location | The user is operating from a location previously used by a different person. |
| Common usage | Common usage detected. |
Was this page helpful?
Thank you. We will use it to improve the documentation. If you want to tell us what is missing or unclear, write to support@ironchip.com.